

The attacks exposed basic security weaknesses in connected refrigeration systems, but experts warn that similar vulnerabilities could put everything from supermarket equipment to hospital and data centre infrastructure at risk.
Cybersecurity researchers say they detected hackers probing internet-connected refrigeration systems across Europe in the days before a wave of cyberattacks and incidents disrupted supermarkets and blood banks, with evidence suggesting it may have been part of a coordinated operation.
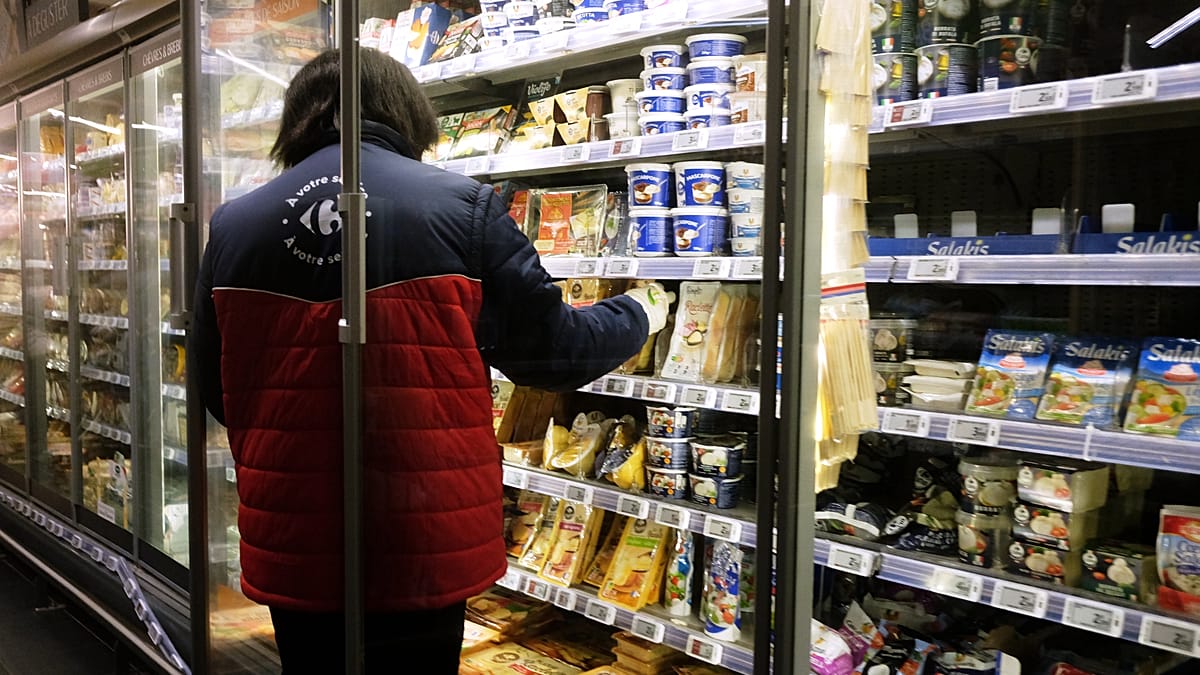
Refrigeration systems in supermarkets across nine European countries as well as several blood banks in France were attacked on 2 and 3 November.
Hackers exploited weak cybersecurity and vulnerabilities in manufacturer Danfoss’s AK-SM refrigeration system manager to put fridges and freezers on defrost settings, in some cases temperatures were set as high 50 degrees Celsius.
The incidents forced many grocery stores to throw away spoiled produce from their fridges and freezers and have become a very visible example of how easily cyberattacks can disrupt everyday life by targeting infrastructure systems that are often taken for granted.
For cybersecurity firm Lupovis, the signs point to a coordinated operation potentially involving a state actor — one that was preceded by days of probing.
The company says it saw a period of reconnaissance targeting these systems just days before the attacks.
The company observed over 276 attempts coming from 91 different threat actors matching specific components of Danfoss controllers during this 10-day period. Activity peaking on 26 October, before coming to a halt at the end of the month.
“Between the 20th and 30th of October, what we saw was a wave of what we call reconnaissance,” CEO Xavier Bellekens told Euronews Next.
“We see a huge peak suddenly for 10 days where adversaries are trying the default passwords. They are trying a couple of those vulnerabilities.”
Lupovis operates a system of so-called “honeypots”, which replicate its clients’ online systems and technologies. The company equips them with sensors and then deliberately exposes them to hackers, encouraging attacks so it can track how these systems are accessed and exploited.
This intelligence can then be used to identify vulnerabilities without putting the clients’ real systems at risk.
It was through this system that Lupovis, whose clients include the Scottish government, Orange, Telefonica and a number of retail companies, detected what it describes as “reconnaissance” on Danfoss systems in the days before November’s attacks.
“You can think of it as like burglars, driving through your neighbourhood and identifying the houses they are going to go and break into,” said Bellekens.
Who was behind the attacks?
Lupovis then traced what it describes as the digital “breadcrumbs” left by the probing and attacks, finding that so-called “bulletproof hosting” was used — web hosting services that are designed to resist takedown requests and law enforcement intervention.
“On the one hand, you have Amazon Web Services, they are the opposite of a bullet-proof hosting. If you do something malicious with one of their servers, that’s it, they cancel your account. Bulletproof hosting is the opposite. You do something malicious, It’s out of jurisdiction,” Bellekens said.
Lupovis then examined the hosting providers themselves.
“We realised that some of those bulletproof hosting had been used by Russian groups in the past,” says Bellekens.
The company is clear that just because servers are located somewhere does not necessarily mean that the people using it share the same nationality, so they cannot say for sure that Russia is behind the attacks.
“However, there’s a bit of a pattern here,” says the Lupovis CEO, “So we are looking for someone that has the capability to attack certain countries in particular.”
According to the CEO, Lupovis sensors in South America, Africa, North America and Asia did not record the same activity. It was only picked up by sensors in Europe.
He also believes the ability to coordinate attacks across Europe helps narrow down the list of suspects.
“You [the attacker] have to be able to coordinate this attack because most of it happened within a 24-hour period.”
“All of this makes us point to an adversary that, to us, is not a script kiddie [an unskilled amateur]. They are not a lone wolf. It looks like a well-planned operation. So a state fits the bill.”
“When we pull on the thread it does look like it could well be Russia. So, that is basically where we’re at.”
The incidents come amid wider concerns about hybrid threats and suspected Russian-linked activity targeting European countries.
However, the precise identity and motivation of the attackers remain unclear.
George Nott, technology editor at The Grocer, said the attacks appeared to have relied on relatively basic security weaknesses rather than highly advanced hacking techniques.
“Attackers managed to access refrigeration systems by simply finding their log-in pages on the open internet, and exploiting already patched vulnerabilities and weak passwords rather than some highly advanced technology,” he told Euronews Next.
Nott also cautioned against drawing firm conclusions about who was responsible.
“it’s still unclear who was behind the attack or what they hoped to achieve. We’ll have to face the fact we may never known. With no ransom demand or claim of responsibility, it could have been anyone from a state-sponsored actor to a gang of teenagers ‘doing it for the lols’.”
Cybersecurity agencies in the countries affected this week have differed in how they describe the incidents. Belgium, Luxembourg, Italy, Portugal and Estonia have called them a “cyberattack”, while Sweden and Ireland referred to it as a “cyber incident”.
The European Union’s Agency for Cybersecurity (ENISA) has also stopped short of explicitly calling the incidents a cyberattack.
How did the hackers access the refrigeration systems?
Hackers were able to access refrigeration systems across Europe because controller boxes connected to the internet were being used to remotely manage refrigeration units, Bellekens said.
Remote control of such devices is common in today’s increasingly digital world. However, the Lupovis CEO says many of the systems could have been better protected had they been placed on virtual private networks (VPNs) rather than exposed directly to the internet.
“[It] would have entirely mitigated the risk because like a VPN is more complex to exploit,” he said.
To make matters worse, many of the systems were reportedly accessible using factory-default credentials, such as “Username” Supervisor” and “Password: 12345”, suggesting that basic security measures had not been implemented.
Nott said the problem reflets a wider tendency in the retail sector to overlook the security of connected equipment.
“The security of connected equipment across the retail sector can overlooked — the priority given to more obvious targets such as payment systems and customer data,” he said.
Once hackers had gained access to the refrigeration control systems they were able to switch them to defrost mode and ramp up the temperatures, spoiling goods stored in fridges and freezers across Europe.
Could other connected infrastructure be next?
The attacks have raised concerns about the security of other internet-connected equipment, from supermarket machinery to the systems that control access, heating and ventilation in buildings.
Nott warned the future attacks may not be confined to refrigeration systems.
“more and more of the systems that keep supermarkets running — heating, ventilation and air conditioning systems; electronic shelf labels; floor cleaning robots — could all present similar vulnerabilities if remote access isn’t properly secured and software patched,” he said.
But the potential exposure goes well beyond retail.
“The freezer is not special. It is just the most visible example of a much bigger category,” says Kumar Sokka, CEO of Acre Security, a global provider of integrated physical security.
“The same kind of small, internet-connected controller that was used to warm up those fridges also runs the doors, the access-control readers, the cameras, the alarms, the lighting and the heating and ventilation in most modern buildings.”
Sokka said the same weaknesses could affect logistics and warehousing, healthcare, manufacturing and data centres, particularly where connected equipment has been introduced without sufficient oversight.
“In an office, a hospital or a data centre, the same kind of compromise might be a door that opens, a camera that goes dark or an alarm that stays silent, and there would be no spoiled stock to tell anyone something was wrong,” he said.
The risk is particularly significant for systems where a digital intrusion can have immediate physical consequences, he added.
Why are these systems still vulnerable?
Despite existing European cybersecurity rules, Sokka said organisations often fail to treat connected physical systems as part of their wider security responsibilities.
The EU’s NIS2 Directive requires organisations within its scope to manage risks to their network and information systems, including through security measures, asset management and incident handling.
However, Sokka said many organisations still focus their compliance efforts on traditional IT systems, leaving refrigeration and other and building systems to facilities management teams.
“A lot of organisations still scope their NIS2 work around classic IT, the servers, laptops and email, and leave the refrigeration, the access control and the building systems to the facilities team, as maintenance rather than security,” he said.
He argued that the problem was not necessarily a lack of regulation, but a failure to apply existing requirements to connected physical infrastructure.
“The regulation is not really the missing piece. The missing piece is the is treating these physical systems as part of the attack surface the regulation is already asking you to protect, and giving someone clear ownership of them.”
Could AI make future attacks easier?
Cybersecurity experts also warn that advances in artificial intelligence could make it easier to identify weaknesses in connected devices and potentially accelerate the development of new attacks.
“AI is collapsing the time between finding a vulnerability and turning it into a working attack,” said Gianni Cuozzo, founder and CEO of Italian cybersecurity firm Exein.
He warned that manufacturers of connected devices may struggle to patch, test and redeploy at the same speed that vulnerabilities are discovered.
“The systems I would worry about most are connected devices that stay in the field for years and can be controlled remotely: refrigeration, building controls, industrial equipment, healthcare systems, data centres and parts of energy and transport infrastructure.”
Cuozzi said organisations should not rely on patching or network protection alone, arguing that connected devices also need to be able to identify and block malicious behaviour themselves.
“Every device needs to be able to defend itself at runtime and pre-emptively block behaviour it was never supposed to perform, whether or not a patch exists and whether or not the vulnerability is already known.”
Source: www.euronews.com
